
PCI Compliance & ASV Scanning Articles
Practical guidance on PCI DSS 4.0.1, quarterly ASV scanning, scope and payment security, written by a PCI Approved Scanning Vendor. Learn what your acquiring bank expects, why scans fail and how to pass them.
48 posts
How to Reduce PCI DSS Scope: What Actually Takes a System Out of the CDE
PCI DSS scope is a documented decision, not a line on a diagram. Learn how to reduce PCI DSS scope and the five evidence items that make an out-of-scope claim survive assessor review.
Why Your PCI DSS Scope Is Bigger Than Your Diagram Says
PCI DSS scope is a documented decision, not a line on a network diagram. This post covers how to determine and prove the CDE boundary, what 12.5.2 requires of the far side of that boundary, and who decides it in 2026.
PCI DSS Compensating Controls: Why the Worksheet Fails Before the Control Does
Most compensating control submissions fail in the constraint field, not the control. We break down the 4 failure modes and the 4-question self-test to run before your assessor sees the worksheet.
What Happens When You Miss a Quarterly PCI ASV Scan
A missed quarterly PCI ASV scan leaves a gap in your attestation file that cannot be cured retroactively. This post covers what the lapse means for your compliance status, and the 5-step plan to close the gap.
Buy a PCI Scan Online: 7 Things to Check Before You Pay
Buying a PCI scan online takes minutes, but not every plan produces a valid ASV attestation. Check these seven things, from scope counting to rescans, before you pay.
Your acquiring bank or payment processor said you need a quarterly AoSC and ASV scans… now what?
Understand quarterly ASV scan AoSC requirements to maintain PCI compliance and protect your ability to accept card payments.
PCI Scan Cost 2026: How Much Does PCI ASV Scanning Cost?
How much does a PCI scan cost in 2026? View Clone Systems PCI ASV scan pricing, with annual packages starting at $185/year.
PCI PTS HSM v5.0: What the New PCI Update Means for Payment Security
Explore the major updates in PCI PTS HSM v5.0, addressing cryptographic practices and emerging security threats for payment systems.
Turning Compliance into a Profit Center: How Enterprises Can Monetize PCI ASV Scanning in 2026
Understand the importance of white label PCI ASV scanning in today’s security landscape for enterprise-level organizations.
Why a Vulnerability Scan Doesn’t Automatically Make You PCI Compliant
A vulnerability scan alone doesn't satisfy PCI DSS. Learn why you need an Approved Scanning Vendor (ASV) and what to ask your provider.
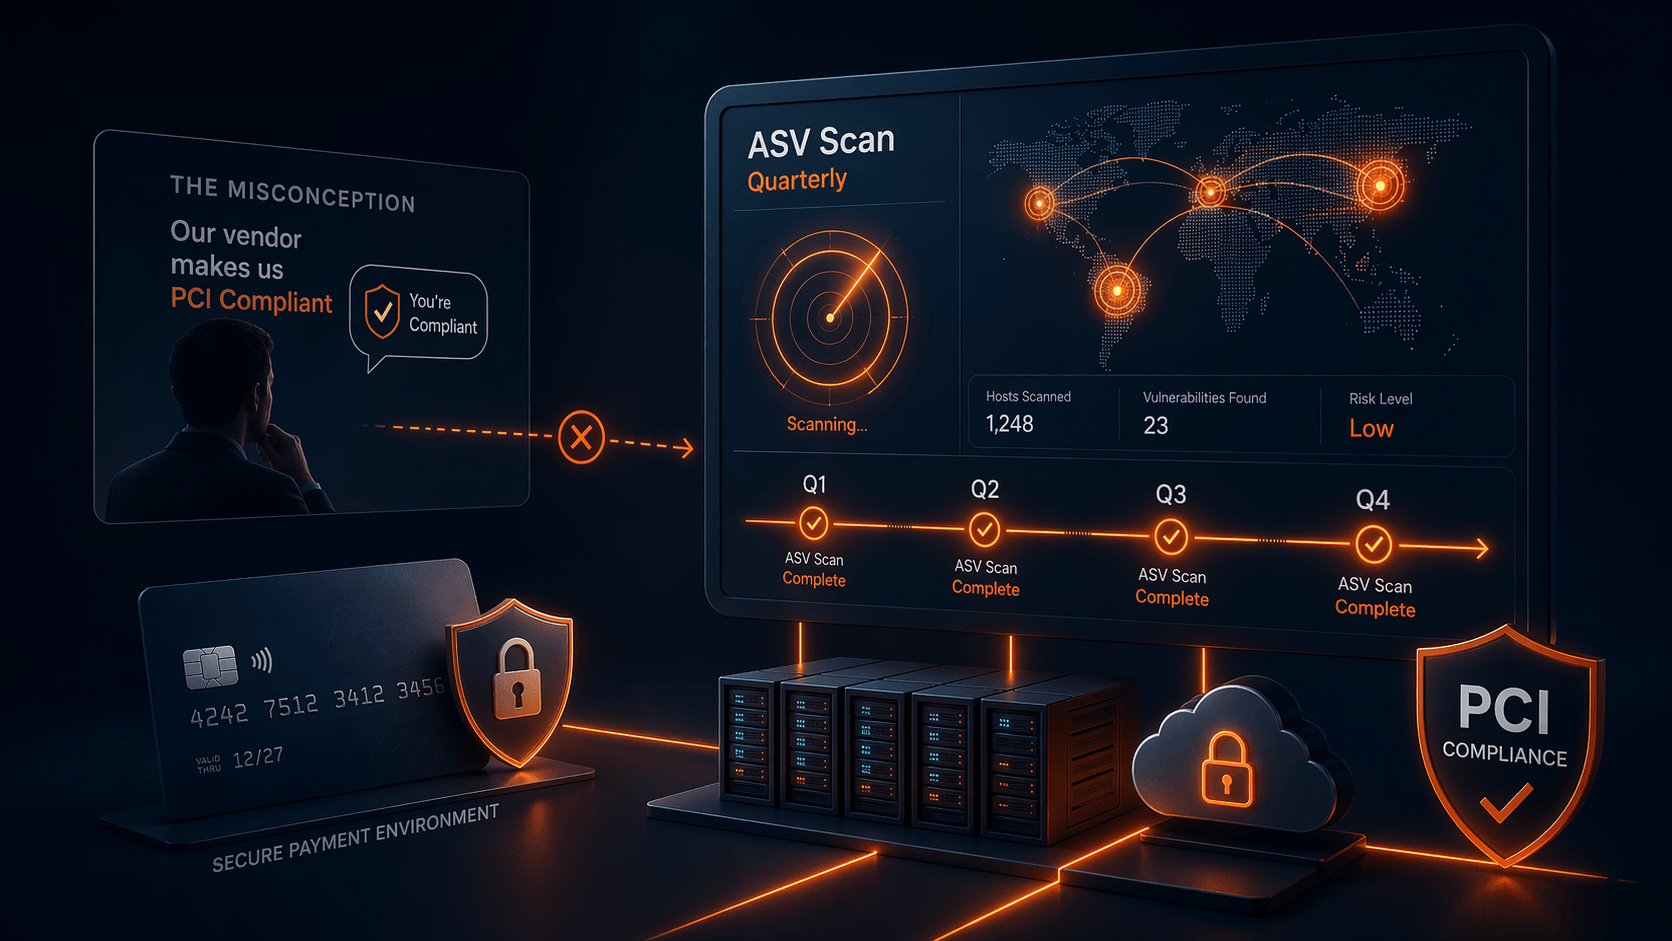
Mastering PCI ASV Scanning in a World That Changes Overnight
Master the essentials of PCI ASV scanning and keep your data secure with timely assessments in today’s fast-paced tech world.
Your Payment Provider Handles Checkout. So Why Are You Still Being Asked for an ASV Scan?
Learn about the importance of the payment provider ASV scan and how it relates to PCI DSS compliance for merchants.
PCI Scan Failed? What to Fix Before Your Next ASV Scan
Most ASV scan failures come down to the same handful of issues. Here is what typically breaks and how continuous scanning keeps you from repeating the cycle.
PCI Scanning Guide 2026: ASV & Authenticated Internal Scans
Guide readers through building an ASV program that pairs external scans with authenticated internal scans and continuous monitoring.
When Machine Learning Joins the Attackers: A Compliance Perspective
Discover the relationship between AI powered cyberattacks and PCI compliance, and how to safeguard your organization against new threats.
Passkeys and Passwordless Authentication: A PCI Perspective on Identity
Passwords are the number-one entry point for attackers. See how passkeys and passwordless authentication satisfy PCI requirements while shutting down credential phishing.
PCI 4.0.1 – A Year in Review & What’s Next for Compliance
PCI DSS 4.0.1 tightens the screws again. Get a plain-English rundown of what changed, what is coming next, and why zero-trust and quantum readiness matter now.
5G & Edge Payment Security: Protecting IoT Terminals & Edge Nodes
5G pushes payment processing to the edge, and attackers with it. How encryption and edge monitoring keep transactions safe.
What Is an Approved Scanning Vendor (ASV) & Why It Matters
Not sure what an ASV actually does? Here is a plain-English breakdown of the role in PCI compliance and how the right vendor keeps your assessments accurate.
PCI DSS for Startups: The Compliance Playbook for Fast Growth
Startups feel PCI is a distraction until it blocks a deal. Use this roadmap to bake segmentation and automated monitoring into your product from day one.
Common Reasons for PCI ASV Scan Failures & How to Resolve Them
The same handful of misconfigurations cause the majority of scan failures. See the top offenders and the exact remediation steps to clear them for good.
Simplifying PCI ASV Scanning for Multi‑Location Hospitality Brands
Scanning dozens of sites turns compliance into a full-time job. See how centralized management and automation turn multi-location ASV programs into a single workflow.
Hidden PCI Risks of Connected Cars: Why In‑Vehicle Payments Need More Than a PIN
Connected vehicles are rolling networks with real payment surfaces. Learn where the risks concentrate and how MFA and secure hardware close them.
The Quantum Clock Is Ticking: Why Payment Processors Must Prepare Now
Quantum-resistant cryptography is no longer optional for payment processors. See what crypto-agile infrastructure looks like and how to plan the transition.
How Payment Gateways Can Support Merchant PCI Compliance More Effectively
Merchants judge gateways on security as much as fees. See how built-in scanning, tokenization and merchant education turn security into a competitive advantage.
Shadow IT: A Compliance Risk That’s Often Missed
Shadow SaaS and unmanaged devices quietly break your PCI scope. Learn how discovery tools and governance policies bring them back under control.
How Payment Processors Can Simplify PCI Compliance Without Compromising Security
Reducing PCI scope should not reduce security. See how tokenization, hosted payment pages and automated scanning shrink your footprint while raising the bar.
Fintech in 2025: Fast Money, Smarter Security
Real-time payments leave no time for manual review. See how AI-driven fraud detection and compliance automation help fintechs move fast without breaking trust.
Breaking Down PCI PTS POI v7.0: Smarter Standards for Safer Payments
PCI PTS POI v7.0 raises the bar for payment devices. Here is a plain-English breakdown of the encryption and tamper-resistance changes and what they mean for you.
Understanding Load Balancers in PCI ASV Scanning
Load balancers can silently hide vulnerabilities from your ASV scans. Learn how they distort results and how to bring them properly into scope.
Why Whitelisting Your ASV Scanner Is the Key to a Valid PCI Scan
Failed ASV scans are often a whitelist problem, not a security one. See why scanner IPs need explicit access and how to configure it without weakening your defenses.
PCI Compliance for the 2025 Vacation Season: Secure Travel & Retail Merchants
Peak season is peak risk for travel and retail merchants. Use these terminal-hardening, encryption and training tips to protect transactions when it matters most.
Making Sense of PCI ASV Reports: A Practical Guide for Compliance Teams
ASV reports can feel like a wall of red text. Follow this step-by-step guide to interpret findings, prioritize what matters and remediate with confidence.
Preparing for Your First Full PCI DSS v4.0.1 Assessment
A PCI assessment is won or lost in the months before the auditor arrives. Use this gap analysis, documentation and monitoring checklist to walk in prepared.
AI’s Expanding Role in PCI DSS Compliance: A Look at PCI SSC’s New Guidelines
Where AI delivers real value in PCI compliance work, and how the latest PCI SSC guidance on AI governance shapes deployments.
Protecting Payments from Smishing Scams: How PCI DSS 4.0.1 Helps
Smishing turns every phone into an attack surface. Learn how modern SMS-based attacks work and which PCI controls actually reduce the risk.
Tap to Pay, Tap to Hack? Understanding Security Risks in Contactless Payments
Contactless payments are convenient for customers and attackers alike. See where the real NFC risks live and how tokenization and EMV standards keep transactions safe.
Strengthening API Security in the Age of PCI DSS v4.0.1
PCI DSS is catching up to how APIs actually break. See how strong authentication, schema validation and anomaly detection combine to satisfy modern requirements.
Quantum Computing and PCI DSS 4.0.1: What It Means for Credit Card Security
Everything you encrypt today can be harvested and decrypted tomorrow. Learn how quantum computing changes the threat model and what post-quantum cryptography does about it.
The True Cost of PCI DSS 4.0.1 Non-Compliance: Fines, Risks, and What You Need to Know
Non-compliance is not just a fine. See the full cost picture, from breach remediation to lost customer trust, and why continuous monitoring pays for itself.
PCI DSS SAQ A Update: Changes We Didn’t See Coming
SAQ A just got more demanding, especially around multi-factor authentication. Here is what changed and a practical path for merchants to comply without disruption.
Debunking the Most Common PCI Compliance Myths
Two common myths, outsourced payments equal no risk and scanning alone equals compliance, cause real breaches. See where responsibility actually sits and how to close the gap.
Leveraging AI for Smarter PCI DSS Compliance
Policy sprawl and manual scan review burn out compliance teams. See how AI automates the tedious work so people focus on judgment calls that actually matter.
Segment Smarter, Not Harder: A PCI DSS 4.0 Roadmap
Good segmentation shrinks PCI scope without turning your network into a maze. Get the practical patterns that reduce audit surface while keeping operations simple.
The New PCI DSS Standards for Safer Payment Pages
PCI now expects real oversight of every script on your payment page. See what integrity checks and real-time monitoring look like in production.
Beyond the Audit: Continuous Monitoring for PCI DSS Compliance
Annual audits catch yesterday's problems. See why continuous monitoring and AI-driven analytics have become the baseline for staying compliant between assessments.
What Is a PCI Approved Scanning Vendor (ASV)?
An ASV is a company approved by the PCI Security Standards Council to run the external vulnerability scans PCI DSS requires every three months. Clone Systems has held ASV status since 2007.
PCI DSS Requirements
PCI DSS does not have to feel like a maze. Get a concise walkthrough of the core requirements and the practical controls that satisfy each one.