
AI Security Articles
How AI changes both sides of security: securing AI agents and LLMs, defending against deepfakes and AI-driven attacks, and putting AI to work in detection and response.
17 posts
AI Agent Authorization: Why Your Workflow's Service Account Is the Attack Surface
AI agent authorization breaks when a workflow executes downstream actions with the service account's authority instead of the requester's. The 5-point check below closes the gap that prompt injection filters miss.
Are AI Agents in PCI DSS Scope? The Test Isn't Whether They See Card Numbers
PCI DSS scope for AI agents is decided by CDE connectivity and security impact, not by whether the agent ever sees a card number. Here is the test, and the evidence a QSA will accept.
Why Your Vulnerability Management Program Can't Score a Prompt Injection Finding
Prompt injection and tool-call abuse findings rarely fit CVE-based vulnerability management. Here's why they get dropped, and a framework to score them instead.
What the OpenAI Security Incident Teaches About AI Security
An AI model chained a zero-day and stolen credentials to reach production infrastructure on its own. Here is what that means for every organization deploying AI assistants, agents, and integrations.
How AI Is Shrinking the Window to Fix Vulnerabilities
Explore the AI vulnerability remediation window: shortening timelines for critical flaws in the age of advanced AI.
The Rise of AI‑Powered Crimeware: Fraud as a Service
Explore the risks of deepfake identity fraud enterprise and how AI is changing the trust landscape in digital interactions.
The Deepfake Deluge: Rebuilding Identity Security for the AI Era
Understand how AI deepfake identity verification challenges traditional methods of establishing trust online and protecting identities.
Guarding Against Prompt Injection: Securing LLMs & AI Agents
Prompt injection is quickly becoming the new SQL injection. Learn how attackers manipulate LLMs and the input validation and context isolation patterns that stop them.
The Agentic AI Frontier: Securing the Autonomous Workforce
Autonomous AI agents move fast and touch sensitive systems. Here are the access controls, human oversight and monitoring guardrails that keep them from going off script.
Why AI‑Driven Attacks Make AI‑Driven Defence Inevitable
Attackers are already using AI. Here is how AI-driven detection, SOAR and threat intelligence keep defenders on the offensive side of the arms race.
Deepfakes & Social Engineering in Financial Services
Deepfakes and voice cloning are now standard tools for financial fraud. Learn how AI-based verification and targeted awareness training close the trust gap.
Quantum Computing Threats to Encryption: Post‑Quantum Algorithms & AI SIEM
Quantum computing will break the encryption we rely on today. See what post-quantum algorithms and AI-driven SIEM look like in practice, and how to start preparing now.
What Every Business Can Learn About Adopting AI the Right Way
Responsible AI adoption is a security decision, not a policy exercise. Get practical guidance on risk assessments, governance and secure model training.
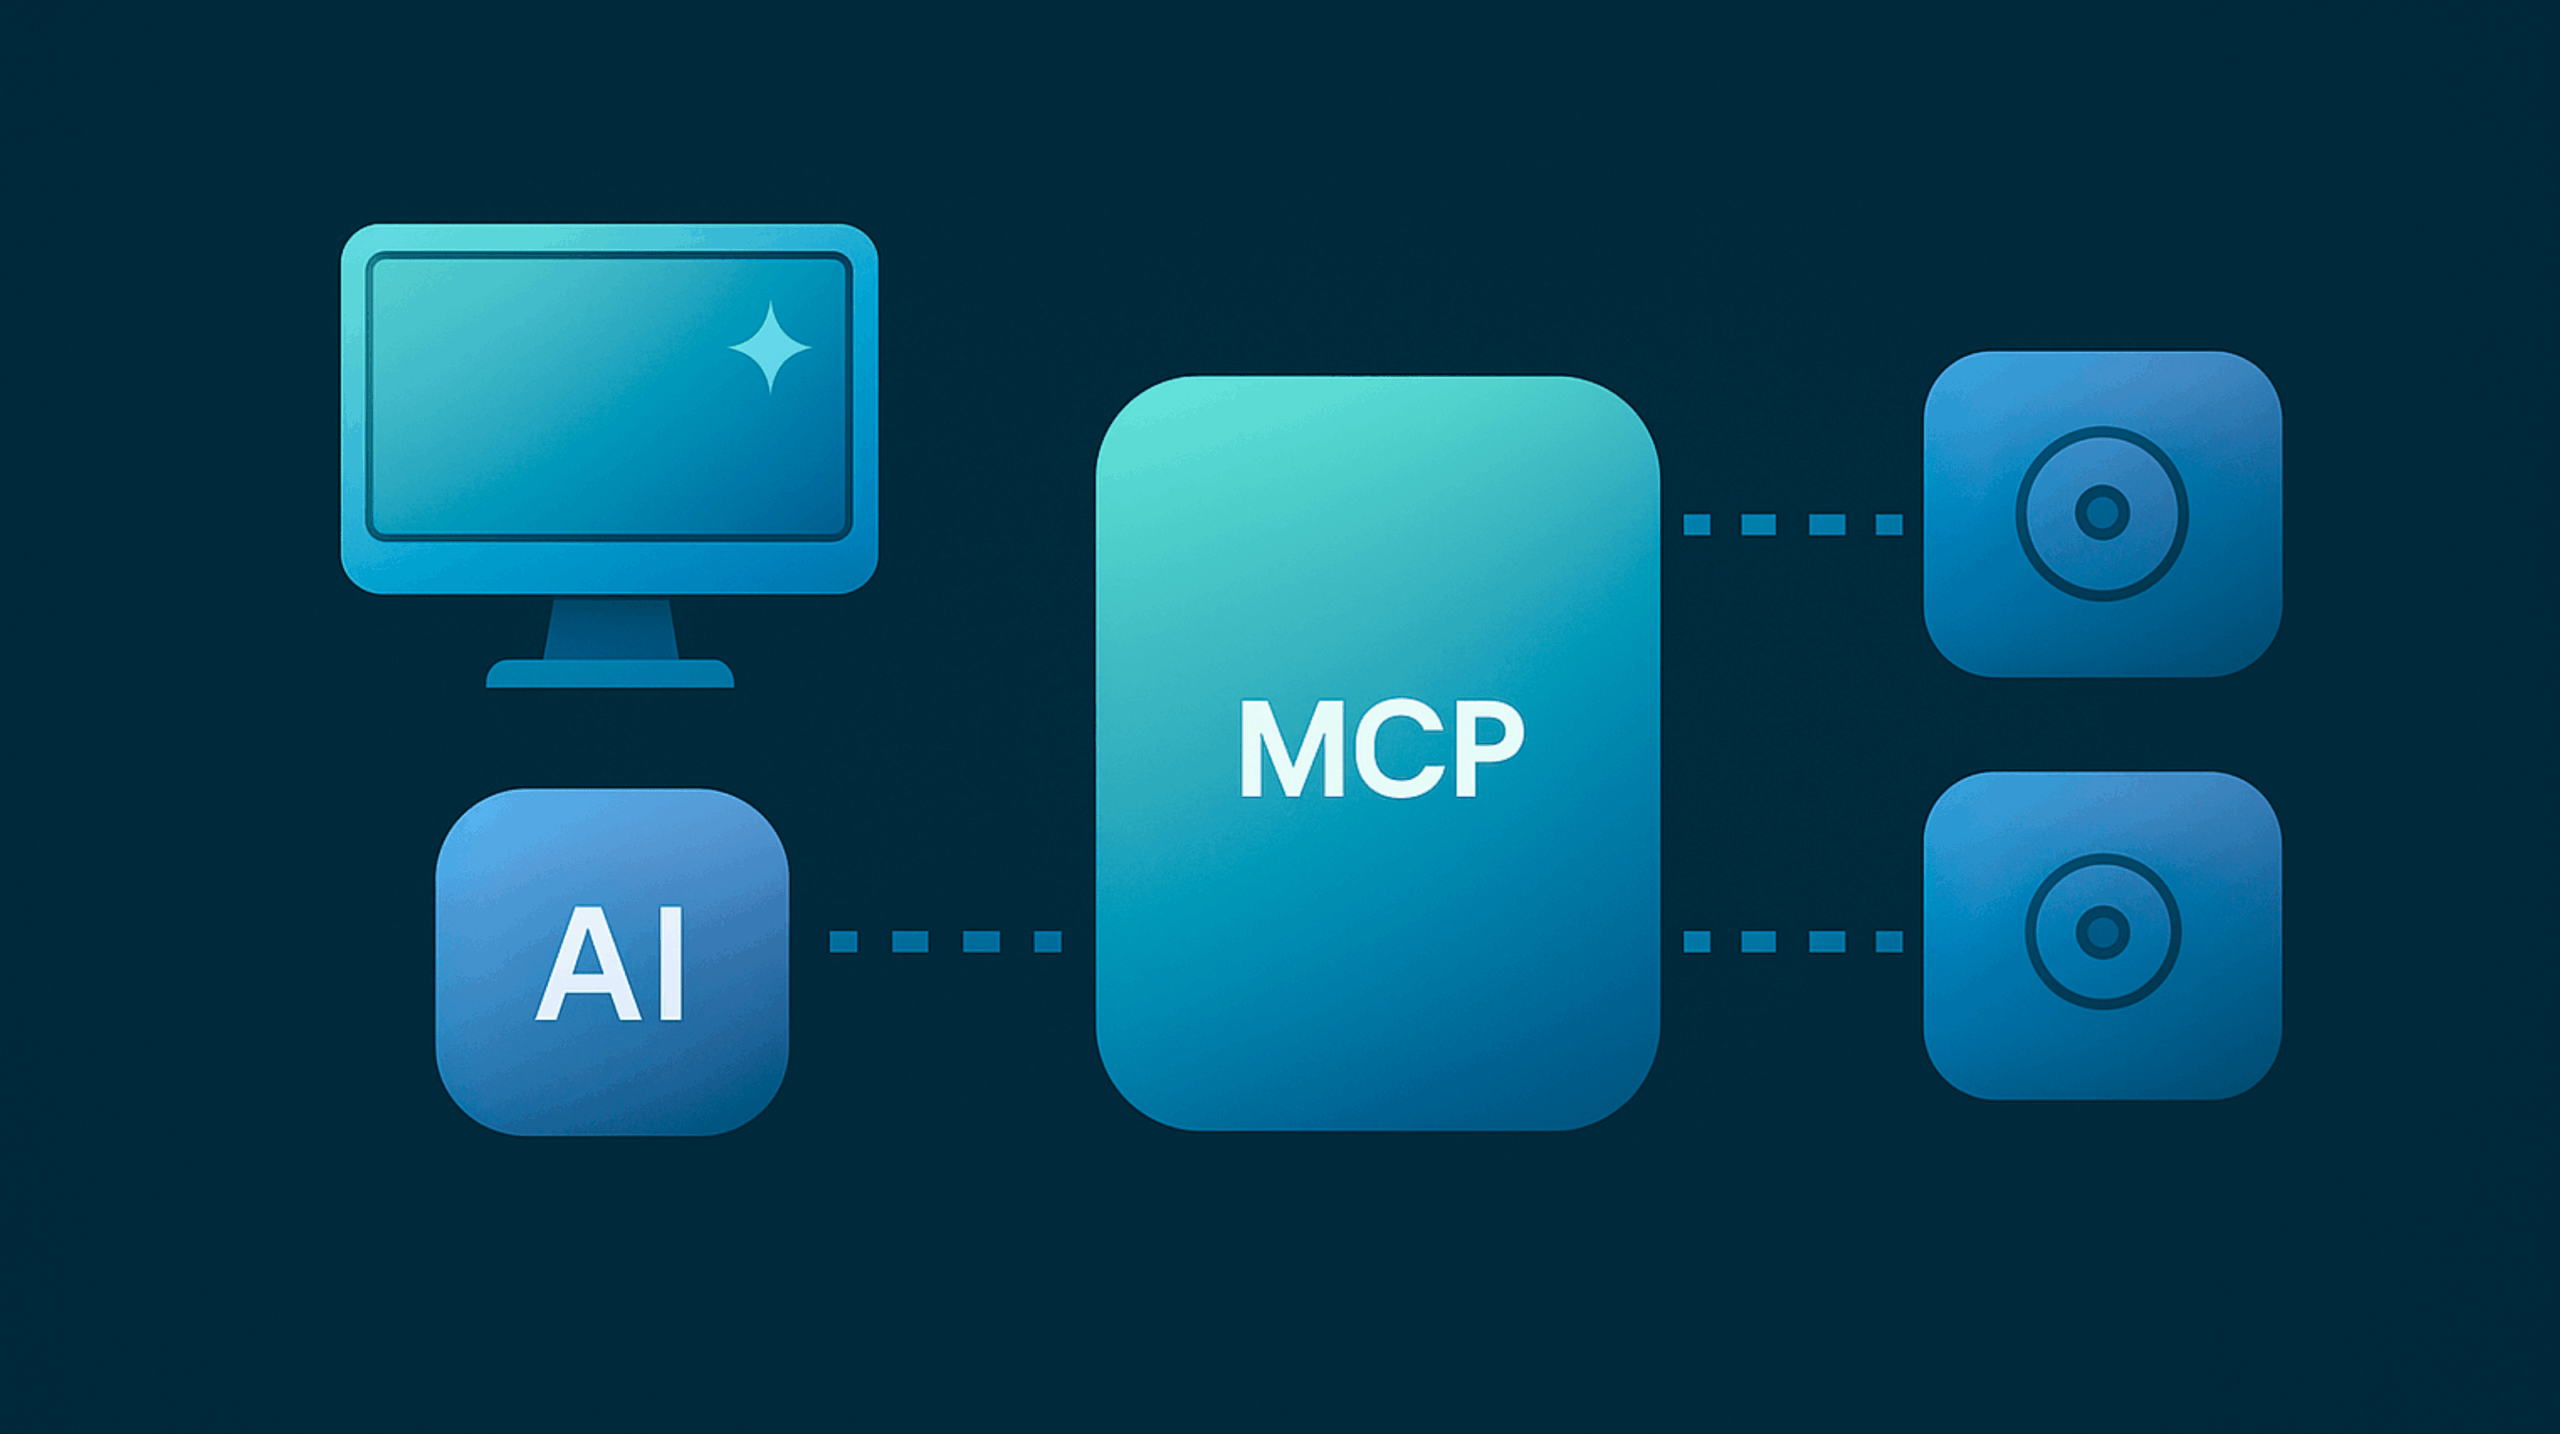
MCP Servers in Agentic AI: What They Are and How to Secure Them
MCP servers give agentic AI real hands on your systems. Understand the risks and the segmentation and monitoring controls that keep agents safely in bounds.
Countering AI Deception: Defending Against Phishing, Voice Cloning & Deepfakes
AI-generated phishing and voice cloning defeat old-school user training. Learn how to spot the new signals and pair AI detection with education that actually sticks.
Guarding the Digital Supply Chain: AI Attacks, SBOMs & Third‑Party Risk
Your vendors are now part of your attack surface. See how SBOMs and continuous vendor monitoring surface the supply-chain risk your own scanners cannot see.
AI in Cybersecurity: The Double‑Edged Sword
AI-enabled threat detection is powerful and easy to over-trust. See where it excels, where it fails, and how human oversight keeps the balance right.